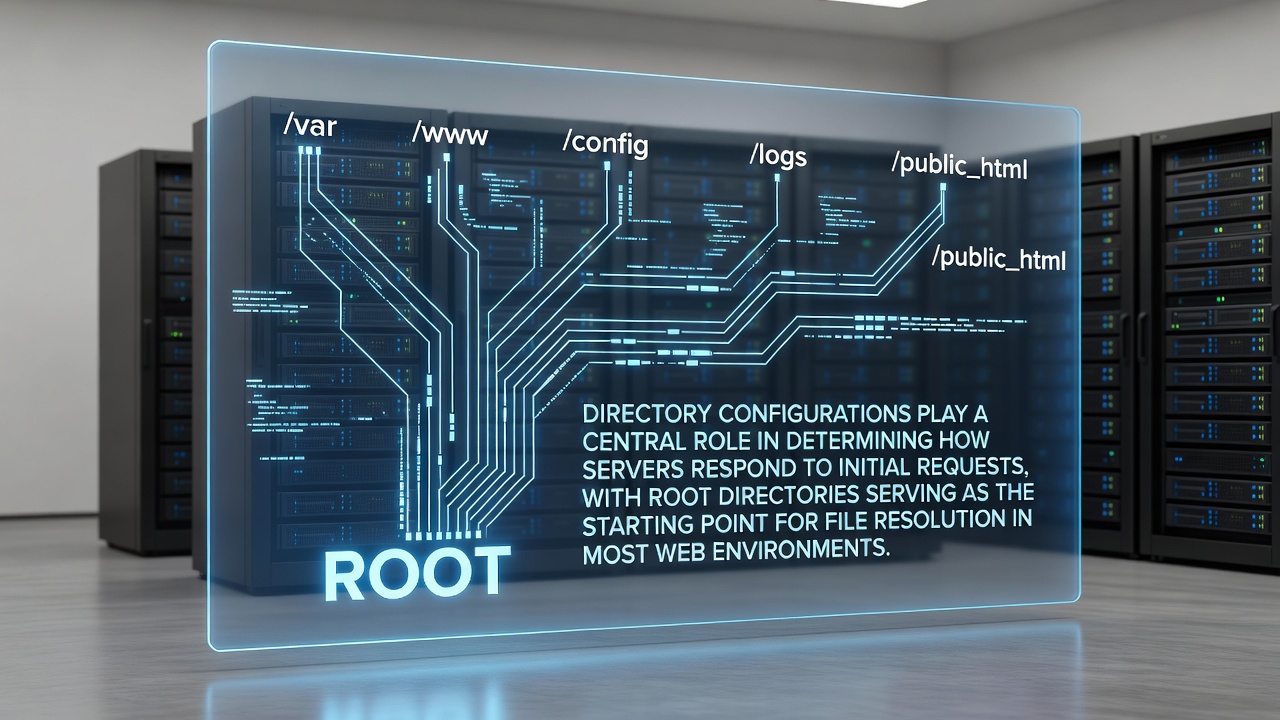
Directory Configurations and Their Impact on Server Request Handling
Directory configurations shape the way servers process incoming requests from the very first interaction, and root directories function as the foundational layer where file resolution begins across most web setups. Web servers rely on these structures to locate resources quickly, map URLs to physical files, and apply access rules without unnecessary delays. Researchers from various institutions have documented how precise directory setups reduce latency during initial handshakes, while misconfigurations often lead to fallback behaviors that affect overall performance metrics.
Core Mechanics of Root Directory Resolution
Root directories serve as the base path that servers consult when an incoming request arrives without a specific subdirectory reference. In standard configurations, the server software checks this location first, then traverses subfolders according to predefined rules that administrators establish during setup. Data from industry reports indicates that over 80 percent of common web environments default to this approach, allowing for consistent handling of requests that target the primary domain or IP address. Observers note that this method keeps resolution paths straightforward, although complex applications sometimes layer additional logic on top to handle dynamic content generation.
Administrators configure these settings through files such as httpd.conf in Apache environments or similar directives in other server software. The process involves specifying the DocumentRoot parameter, which points directly to the folder containing initial files like index pages. Studies show that clear separation between system files and user-accessible content within the root helps maintain security boundaries, and this practice appears in guidelines published by organizations focused on web infrastructure standards.
Server Response Patterns Influenced by Directory Layouts
When a request reaches the server, the directory structure determines whether the system serves a static file, executes a script, or returns an error code. Root-level placements often trigger default behaviors, such as loading an index.html or index.php file automatically. Those who manage large-scale deployments report that grouping related assets under clear subdirectories speeds up this resolution, because the server avoids exhaustive searches across unrelated folders. Evidence from technical documentation reveals that hierarchical arrangements also support better caching strategies, since content in predictable locations receives consistent treatment during repeated accesses.
Additional factors come into play with virtual hosts, where multiple sites share the same server yet maintain separate root directories. This separation ensures each domain resolves files independently, preventing cross-contamination of resources. Research indicates that such isolation proves especially useful in shared hosting scenarios, where resource limits and permission sets vary between accounts.
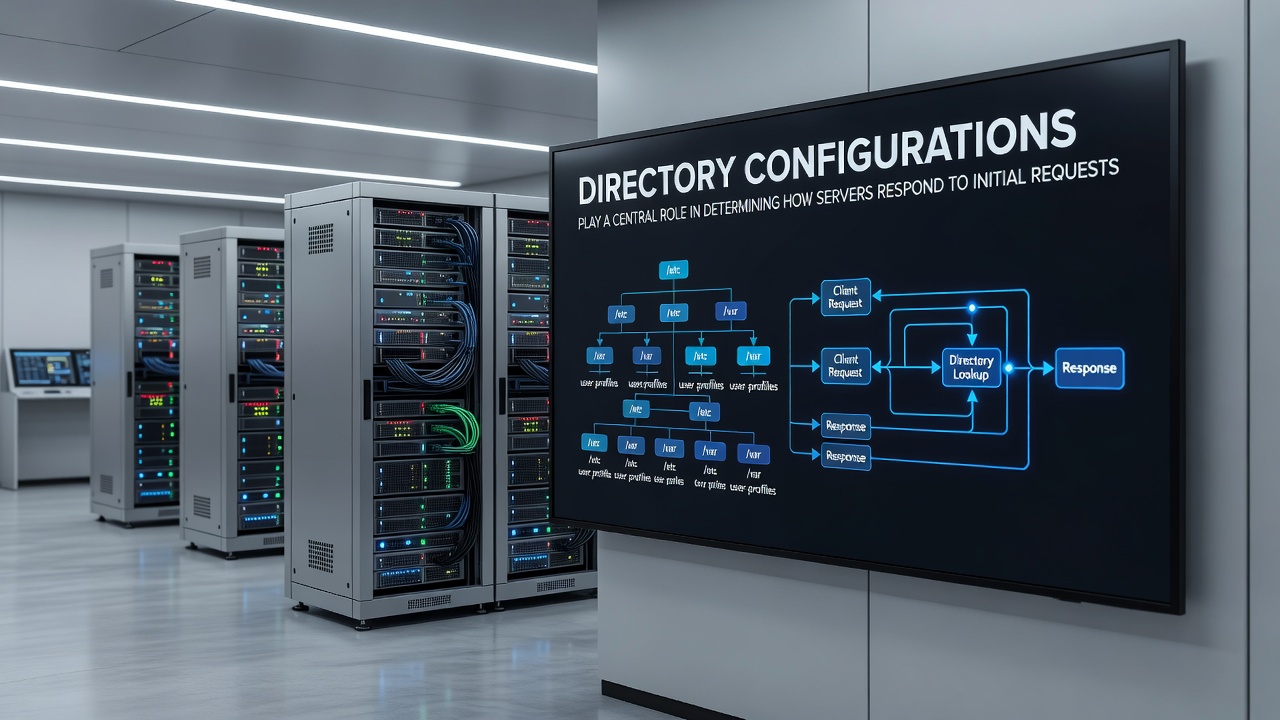
Practical Implementation Across Different Platforms
Platform-specific tools influence how directories integrate with request handling. On Unix-based systems, symbolic links often extend the root directory without moving actual files, while Windows environments rely on path mappings that achieve similar flexibility. According to documentation from the Apache Software Foundation, these techniques allow administrators to reorganize content while preserving external URLs. People managing cross-platform projects frequently combine these methods with environment variables that adapt paths automatically during deployment.
Security considerations remain tied to directory permissions at every level. Root directories typically receive the strictest access controls, limiting write operations to prevent unauthorized modifications. Reports from cybersecurity research groups highlight cases where overly permissive root settings contributed to vulnerabilities, underscoring the need for regular audits. In September 2026, ongoing updates to server software continue to emphasize hardened defaults that restrict root-level exposure by default.
Advanced Configurations and Their Effects
Beyond basic setups, rewrite rules and alias directives modify how servers interpret paths that start from the root. These tools let administrators redirect requests or mask internal structures without altering the visible URL scheme. Data collected by web performance monitoring services shows measurable improvements in load times when such rules streamline resolution for frequently accessed resources. Yet overly intricate configurations can introduce their own processing overhead, which becomes noticeable under high traffic volumes.
Containerized deployments add another layer, where root directories exist within isolated environments rather than on the host system. This approach maintains consistency across development, staging, and production stages. Academic papers from computer science departments at multiple universities describe how these practices reduce configuration drift and simplify scaling operations.
Conclusion
Directory configurations ultimately dictate the efficiency and reliability of server responses from the initial request onward, with root directories anchoring the entire resolution process. Organizations that invest in clear, well-documented structures benefit from predictable behavior and easier maintenance over time. As web environments evolve, continued attention to these foundational elements supports stable performance across diverse deployment scenarios.